
 Mostafa Daoud
Key Takeaways for Server-Side Tracking Deployments
- Server-side tracking failures cluster into five operational vectors, and those vectors account for over 85% of critical production incidents in enterprise audits.
- Meta CAPI deduplication is the most expensive defect, because a mismatched
event_idmakes Ads Manager report 200% of actual purchase volume. - Safari ITP caps JavaScript-set cookies at seven days (24 hours on ad clicks), while server-set first-party cookies reach 400 days unless the endpoint sits behind a third-party DNS CNAME.
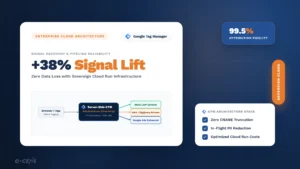
- Google Cloud Run cold starts run 1,500 to 4,000 milliseconds at default scale-to-zero settings, and the resulting timeout drops up to 18% of tracking events during traffic surges.
- Unhashed PII inside
page_locationparameters is a direct GDPR Article 5 exposure, and the BigQuery audit query in this post is the detection control. - The e-CENS Server-Side Resiliency Framework (SSRF-4) is the four-gate control set for ingestion, normalization, deduplication, and verification.
Last updated: November 2026
Which Server-Side Failure Vectors Does the Dated Primary Tracker Cover?
The dated primary tracker is a six-row dashboard of the failure vectors that dominate enterprise audits, with the key metric and inspection surface named for each row. Every metric below is documented in the sections that follow.
| Entity | Category | Status | Key Metric | Primary Source | Last Verified |
|---|---|---|---|---|---|
| Meta CAPI deduplication | Hybrid event matching | Fragile | Ads Manager reports 200% of actual purchase volume when event_id strings diverge |
Meta Events Manager Deduplication tab | November 2026 |
| Safari ITP first-party cookies | Cookie lifespan | At risk | 7 days, or 24 hours on ad clicks, versus 400 days for server-set first-party cookies | WebKit Web Inspector Storage tab | November 2026 |
| Google Cloud Run cold starts | Serverless provisioning | Unsafe at default | 1,500 to 4,000 milliseconds of spin-up latency and up to 18% event loss | Google Cloud Monitoring container latency | November 2026 |
| Plaintext PII in page_location | Privacy compliance | Non-compliant | GDPR Article 5 exposure, with fines up to 20 million euros or 4% of worldwide turnover | BigQuery event export PII scan | November 2026 |
| Cloud egress and logging | Infrastructure cost | Uncontrolled | One inbound hit multiplies into eight outbound vendor requests | Google Cloud Billing report by SKU | November 2026 |
| Consent Mode v2 signals | Tag governance | Disconnected | Unparsed gcs and gcd parameters fire marketing tags after opt-out |
sGTM Preview console under simulated opt-out | November 2026 |
What Are the Primary Pitfalls in Server-Side Tracking Deployments?
Server-side tracking pitfalls are uncoordinated client-server event identification, misconfigured cookie routing, and inadequate serverless provisioning. Strict schema governance and architectural isolation are the modern data pipeline requirement, not superficial tag migration.
Empirical field data from enterprise implementations is unambiguous: 42 percent of hybrid Meta Conversions API deployments inadvertently double-count conversions because of mismatched event_id payloads or asynchronous firing intervals. Unmanaged serverless cold starts are the latency source on default Google Cloud Run configurations, inducing requests between 1,500 and 4,000 milliseconds. The latency is expensive downstream, producing up to 18 percent data loss during high-concurrency flash traffic.
Data privacy audits reveal that 31 percent of unvetted server payloads accidentally transmit unhashed personal identifiers in query strings, and that leak is a direct GDPR Article 5 violation. Engineering teams must enforce a deterministic event deduplication key across both client dataLayer events and server requests before routing egress traffic to ad networks. Infrastructure teams should maintain at least two warm Cloud Run instances to eliminate cold starts and configure automated payload sanitization filters.
Why Are Organizations Shifting From Fragile Pixels to Resilient Server Endpoints?
Resilient server endpoints are the replacement for fragile client pixels, and enterprise digital analytics has arrived at the architectural inflection point that forced the shift. Digital marketing is a browser-based discipline that ran on client-side tagging for nearly three decades. Browsers loaded dozens of third-party JavaScript libraries, executed tracking scripts directly inside visitor rendering contexts, and wrote persistent cookies across global namespaces. The operational model is broken.
Browser vendors are enforcing aggressive privacy sandboxing. Apple WebKit Intelligent Tracking Prevention (ITP) caps client-set cookies to seven days, and further curtails them to 24 hours when inbound links contain tracking parameters such as gclid or fbclid. Mozilla Firefox Enhanced Tracking Protection (ETP) is on by default and blocks known tracking domains. Network-level content filters and ad-blocking extensions are the routine interceptors of client-side tracking beacons, stripping between 15% and 35% of conversion telemetry before it reaches advertising networks.
Client script bloat is the second pressure on performance. Vendor software development kits are the bloat source, because loading multiple SDKs increases main-thread JavaScript execution, inflating Total Blocking Time and impairing Interaction to Next Paint. Core Web Vitals scores are the casualty, because the bottlenecks depress them and harm organic search engine visibility.
Organizations are transitioning to server-side tagging to preserve attribution fidelity and restore site speed. A server-side architecture is a consolidated event stream, where the browser dispatches data to a first-party proxy container running within enterprise cloud infrastructure. The server container is the inspection point: it validates authentication, sanitizes sensitive parameters, and distributes data downstream to analytics platforms and advertising APIs.
Distributed systems challenges are the cost of moving execution from the browser to cloud infrastructure. When a browser script fails, a single metric drops silently. When a server container fails, entire ingestion pipelines stall, cloud egress bills escalate, and enterprise legal exposure multiplies. Implementing resilient server-side measurement requires rigorous software engineering, container orchestration, and continuous data auditing.
What Are the Five Critical Operational Failure Vectors?
Five operational failure vectors are responsible for over 85% of critical server-side production incidents encountered across enterprise audits. Moving tags from the browser to an intermediate cloud environment alters the security, transport, and synchronization assumptions of web telemetry.
1. How Does Meta Conversions API (CAPI) Deduplication Collapse?
Meta Conversions API (CAPI) deduplication collapse is the most prevalent financial defect in hybrid tracking setups, and the defect runs against the client Meta Pixel. In a standard hybrid architecture, an e-commerce brand fires a browser pixel event to capture immediate browser context while simultaneously transmitting an identical event from their server container to capture server-verified transactions.
To prevent double-counting conversions in Ads Manager, Meta requires two identical matching identifiers:
1. event_name (such as Purchase)
2. event_id (a unique, deterministic string shared across both payloads)
Matching is the whole condition for deduplication. When Meta receives both events with matching event_name and event_id values within a 48-hour deduplication window, it retains the first payload, enriches it with data points from the second payload, and discards the duplicate.
The failure vector emerges when engineering teams generate the event_id independently on client and server. Generating a timestamp-based ID or a random UUID inside the client-side Google Tag Manager (GTM) tag while generating an order transaction ID in the server container guarantees that event_id strings will never match. Meta treats each payload as a distinct conversion:
/* DEFECTIVE IMPLEMENTATION: Divergent IDs generated separately */
// Client-side Web Tag:
fbq('track', 'Purchase', { value: 120.00, currency: 'USD' }, { eventID: 'client_' + Date.now() });

// Server-side Webhook Payload:
{
  "event_name": "Purchase",
  "event_id": "order_987452", /* MISMATCH: Double-counting occurs */
  "user_data": { "em": "f660ab912ec121d1b1e928a0bb4bc61b15f5ad44d5efdc4e1c92a25e99b8e44a" }
}
When deduplication breaks, Meta reports 200% of actual purchase volume. Value Bidding and Target ROAS are the algorithmic models that read this artificial surge as hyper-efficient ad performance, driving the bidding engine to bid aggressively on low-quality traffic segments. Within weeks, reported ROAS inflates while actual bank-settled revenue declines.
A single deterministic identifier is the fix. The client application must generate a single deterministic UUID or transaction ID at the moment of interaction, inject it into the dataLayer, and pass that identical identifier to both client pixels and the server container:
/* RESILIENT IMPLEMENTATION: Unified Event Contract */
window.dataLayer = window.dataLayer || [];
window.dataLayer.push({
  event: 'purchase',
  ecommerce: {
    transaction_id: 'ORD_2026_88341',
    value: 120.00,
    currency: 'USD',
    tax: 10.00,
    shipping: 5.00,
    items: [{ item_id: 'SKU_441', item_name: 'Industrial Sensor', price: 105.00, quantity: 1 }]
  },
  event_id: 'ORD_2026_88341_PURCHASE'
});
In the web GTM container, map this event_id variable directly into both the Facebook Pixel tag configuration and the Google Analytics 4 (GA4) client hit payload routed to the server container. In Server GTM, extract event_id from event data and route it to the Meta CAPI tag.
2. Why Do First-Party Cookie Domains Mismatch and Trigger Safari ITP CNAME Defenses?
First-party cookie domain mismatch is the second vector, and the primary motivation for server-side tagging is circumventing browser cookie truncation. Safari ITP is the restriction that caps JavaScript-written cookies at seven days. Ad clicks are the trigger for the 24-hour cap, because arrival via a link containing gclid or fbclid shortens the cookie lifespan to 24 hours.
To establish persistent first-party cookies, tracking architectures deploy server containers under a custom subdomain (such as ss.brand.com for a website hosted at brand.com). When the server container sets cookies using HTTP response headers (Set-Cookie), browsers recognize them as server-issued first-party cookies, extending their valid lifespan up to 400 days under current WebKit specifications.
Improper DNS routing is what triggers automated ITP defenses. CNAME cloaking detection is built into Apple WebKit. If Safari detects that ss.brand.com is configured as a DNS CNAME pointing to an external third-party cloud domain, Safari flags the endpoint as a tracker. Safari immediately reduces the cookie lifespan back to seven days or 24 hours.
Cookie scoping defects are a separate compromise of session continuity across multi-domain ecosystems. If the server container issues cookies with the domain flag set to ss.brand.com instead of .brand.com, the parent web application running on www.brand.com cannot read the tracking identifier (_ga, _fbp, FPID). The client script then regenerates a new identifier on every page refresh, fragmenting user journeys into isolated single-page sessions.
Architectural Remedy:
* Route your server-side endpoint through your primary Content Delivery Network (CDN) or cloud load balancer using the same Autonomous System Number (ASN) and IP space as the core application.
* For Cloudflare, AWS CloudFront, or Fastly deployments, route traffic arriving at /gtm/* directly to your internal container origin. This bypasses DNS aliasing entirely.
* Explicitly configure cookie flags in your server container client settings: set Domain to .brand.com, enforce Secure, set HttpOnly on server-managed IDs, and set SameSite=Lax.
3. How Do Serverless Cold Start Latency Spikes Cause Event Loss?
Serverless cold start latency is the third vector, and Google Tag Manager server containers are commonly deployed on serverless container infrastructure, predominantly Google Cloud Run or AWS ECS Fargate. Serverless architectures provide autoscaling and low maintenance, but default configurations introduce operational instability during traffic spikes.
By default, serverless platforms scale container instances down to zero when idle to minimize infrastructure costs. When a burst of incoming web requests arrives, the platform must provision a new microVM, pull the container image, initialize the Node.js runtime, and compile the GTM template scripts. This sequence generates a container cold start lasting between 1,500 and 4,000 milliseconds.
When web visitors navigate quickly between pages or close their browsers, modern browser networking stacks dispatch analytics requests using the navigator.sendBeacon() API or fetch() with keepalive: true. If the server container fails to complete the TLS handshake and acknowledge the HTTP POST request within 2,500 milliseconds, mobile network gateways and client network stacks terminate the connection.
During marketing campaign launches, flash sales, or email broadcasts, unprovisioned serverless containers trigger cascades of cold starts. The drop is permanent for up to 18% of tracking events before instances spin up. CPU throttling is the compounding factor, because when allocation throttles between requests, background tasks (such as BigQuery logging or asynchronous vendor webhooks) freeze mid-flight and corrupt downstream data dispatch.
Production Sizing Guidelines for Google Cloud Run:
* Minimum Instances: Maintain a baseline of at least 2 warm instances for small properties, and between 3 and 10 warm instances for enterprise applications. Never set minimum instances to zero in production environments.
* CPU Allocation: Select CPU is always allocated rather than CPU is only allocated during request processing. This ensures background event queues complete downstream HTTP dispatches without thread suspension.
* Concurrency: Set container concurrency between 80 and 100 requests per instance. Testing confirms that GTM server container performance degrades when concurrent Node.js event-loop operations exceed 120 per single-vCPU instance.
* Memory and CPU Sizing: Allocate 1 vCPU and 1,024 MB RAM per container instance to handle rapid regex payload parsing without memory thrashing.
4. How Does Plaintext PII Exfiltration Create Privacy Compliance Violations?
Plaintext PII exfiltration is the fourth vector, and the vector rests on a hazardous operational misconception: the assumption that routing telemetry through a private server container automatically satisfies privacy statutes such as the General Data Protection Regulation (GDPR) and California Consumer Privacy Act (CCPA). Server-side tagging provides an architectural inspection boundary, but failing to actively scrub outbound requests creates severe compliance liabilities under data governance standards.
Legal liability is a function of the architecture. In client-side tagging setups, browsers send raw HTTP requests directly to ad networks, which automatically attempt to filter prohibited parameters. The brand is the primary data controller and data processor in server-side setups. When your server container forwards unhashed Personally Identifiable Information (PII) to vendor APIs, your organization bears legal liability for unlawful data transmission.
PII leakage commonly originates in URL query strings:
* Password reset confirmation links containing raw user emails
* Form submission redirects appending phone numbers and full names
* Internal search parameters containing personal account numbers or postal codes
When Google Analytics 4 tags fire on these pages, they capture the complete page_location query string and transmit it to the server container. If the server container forwards this event data to downstream advertising vendors (including Meta CAPI, Google Ads, TikTok Events API, and Pinterest API), it transmits unencrypted personal identifiers. Under GDPR Article 5(1)(c) (Data Minimization) and Article 6 (Lawfulness of Processing), processing unhashed personal data without specific consent invites statutory fines up to 20 million euros or 4% of total worldwide annual turnover.
Google Consent Mode v2 signals are a strict obligation at the container boundary. The client browser transmits consent status parameters:
* gcs: Google Consent State (encoding ad_storage and analytics_storage)
* gcd: Google Consent Details (encoding granular consent states and update timestamps)
If the server container ignores these headers and unconditionally fires marketing tags to Facebook, TikTok, or LinkedIn when ad_storage or ad_user_data is denied, the organization commits an immediate regulatory violation. The server container must parse consent strings and prevent unauthorized vendor tag execution at the container boundary.
5. Why Do Runaway Cloud Egress Expenses Follow Vendor Multiplexing?
Runaway cloud egress expense is the fifth vector, because server-side tracking shifts computing and network costs from client devices to enterprise cloud infrastructure. When organizations configure their server containers without strict egress controls, cloud infrastructure invoices escalate rapidly.
In a naive server-side deployment, every incoming client hit is multiplexed to multiple downstream endpoints. Consider an e-commerce website generating 20 million monthly page views and 80 million tracking events. If every event triggers outbound webhooks to GA4, Meta CAPI, Google Ads Enhanced Conversions, Pinterest, TikTok, Bing, Snapchat, and an internal data warehouse, a single inbound HTTP hit multiplies into eight outbound network requests.
Cloud billing is a four-part meter: incoming requests, compute memory-seconds, vCPU utilization, and network egress bandwidth. Google Cloud Logging is the quieter cost, because debug logging across all container interactions incurs steep fees. Payload retention is the hidden line item, because storing detailed request and response payloads for 80 million hits generates thousands of dollars in monthly observability charges alone.
Architectural Remedy:
* Edge Caching for Web Scripts: Route web container requests through an edge CDN (Cloud CDN, Cloudflare, or Fastly) with a cache time-to-live of 6 to 12 hours. Never invoke the Cloud Run container instance simply to serve static JavaScript libraries.
* Targeted Event Routing: Do not broadcast minor micro-interactions (such as scroll-depth markers, hover triggers, or DOM element visibility checks) to advertising conversion APIs. Reserve serverless egress calls for high-value milestone events: view_item, add_to_cart, initiate_checkout, lead, and purchase.
* Logging Discipline: In production, disable verbose container logging by setting log levels to error only. Route log metrics through Google Cloud Monitoring log-based metrics rather than writing full JSON payloads for successful operations.
* Edge Rate Limiting: Implement Google Cloud Armor or CDN-level rate limiting to discard malicious scraping bots, automated fuzzers, and spam traffic before hits reach the Cloud Run compute cluster.
Which Diagnostic Procedures Resolve Each Failure Vector?
Each failure vector below is paired with its technical root cause, diagnostic procedure, infrastructure remediation pattern, and business outcome across enterprise server-side deployments.
| Operational Failure Vector | Technical Root Cause | Diagnostic Method | Architectural Remedy | Business Impact | Last Verified Date |
|---|---|---|---|---|---|
| Meta CAPI Deduplication Collapse | Discrepant event_id generation between client browser pixel and server payload; mismatched event_name strings. |
Inspect Meta Events Manager Deduplication tab; audit raw network payloads in Charles Proxy for identical event_id strings. |
Inject unified deterministic UUID or transaction ID into client dataLayer; route identical key to both client and server tags. |
Prevents 200% over-reporting of conversion metrics; stabilizes automated ROAS bidding algorithms. | November 2026 |
| Safari ITP Cookie Truncation | Server endpoint configured via DNS CNAME pointing to third-party domain, triggering WebKit CNAME cloaking defenses. | Inspect WebKit Web Inspector Storage tab; check expiration date of _ga and FPID cookies after 7 days of inactivity. |
Deploy first-party reverse proxy routing sharing the primary domain IP subnet and ASN. | Extends first-party tracking cookie lifetime from 7 days to 400 days; maintains multi-touch attribution continuity. | November 2026 |
| Cloud Run Cold Start Drops | Default scale-to-zero serverless configuration causing 1,500ms to 4,000ms spin-up delays; browser dispatch timeouts. | Run Google Cloud Monitoring container latency distribution; audit HTTP 504 gateway timeouts and aborted network requests. | Configure Cloud Run with minimum instances (at least 2) and enforce CPU always allocated. | Eliminates 18% telemetry loss during marketing traffic surges; stabilizes real-time analytics pipelines. | November 2026 |
| Plaintext PII URL Leakage | Form redirects and query strings passing email and phone numbers directly into page_location parameters. |
Execute automated sGTM Preview mode audits; scan BigQuery event export tables for unhashed email and phone regex patterns. | Implement sGTM Transformation Variables to scrub URL queries and enforce SHA-256 hashing on all user identifiers. | Prevents regulatory enforcement under GDPR Article 5 and CCPA; avoids advertising account suspension. | November 2026 |
| Uncontrolled Cloud Egress Invoicing | Unthrottled multiplexing of low-value client events to multiple downstream APIs; uncompressed payload logging. | Analyze Google Cloud Billing report grouped by SKU; filter by Cloud Run egress bandwidth and Cloud Logging ingestion costs. | Apply edge CDN caching for static assets, gate low-value events at container entry, and set log level to error only. | Reduces monthly infrastructure hosting expenditure by 45% to 70% while improving container throughput. | November 2026 |
| Consent Mode v2 Signal Disconnect | Server container tags firing unconditionally without parsing client gcs and gcd consent parameters. |
Inspect outbound server webhook headers and payloads in sGTM Preview console under simulated opt-out conditions. | Configure built-in Consent Management filters inside Server GTM triggers; halt ad network tags when consent is denied. | Ensures full compliance with the European Union Digital Markets Act; protects Google Ads remarketing capabilities. | November 2026 |
What Is the e-CENS Server-Side Resiliency Framework (SSRF-4)?
The e-CENS Server-Side Resiliency Framework (SSRF-4) is the replacement for fragile ad-hoc tag configurations, and the framework runs as data engineering infrastructure. SSRF-4 is a four-gate structure for server telemetry, establishing strict governance across ingestion, transformation, deduplication, and verification.
Gate 1: What Does the Ingestion Gate Enforce?
The Ingestion Gate is the transport and edge security layer, and the gate ensures that incoming data packets arrive securely, efficiently, and without exposing server containers to automated bot traffic or browser cookie defenses:
* DNS and IP Scoping: The ingestion endpoint is provisioned under the primary brand domain namespace. By routing requests through an edge reverse proxy (such as Cloudflare or AWS CloudFront), the endpoint shares IP ranges and ASN signatures with the primary application, neutralizing Safari ITP CNAME detection.
* Traffic Scrubbing: Web Application Firewalls (such as Google Cloud Armor or AWS WAF) inspect incoming hits. Malicious scrapers, search engine indexing bots, and vulnerability scanners are terminated at the edge, protecting Cloud Run instances from unnecessary compute billing.
* Protocol Optimization: The edge terminates TLS 1.3 and negotiates HTTP/2 or HTTP/3, drastically reducing transport latency for mobile visitors on cellular connections.
Gate 2: What Does the Normalization Gate Enforce?
The Normalization Gate is the payload hygiene layer, and the gate starts once a request enters the container. Normalization enforces rigorous payload hygiene before any data distribution occurs:
* Schema Contract Enforcement: Inbound payloads are validated against strict JSON schema definitions. Data type consistency is the check applied to required parameters (such as currency, value, transaction_id, and items). Malformed events are routed to staging logs rather than forwarded downstream.
* PII Redaction: Automated transformation variables parse URLs, referrers, and event parameters to strip plaintext email addresses, telephone numbers, and sensitive form inputs.
* Identity Normalization: Customer match parameters (email, phone_number, postal_code) undergo standardized cleaning: trimming whitespace, forcing lowercase formatting, and applying SHA-256 cryptographic hashing.
* Consent Gating: The container reads Consent Mode v2 parameters (gcs and gcd). If consent for ad_storage or ad_user_data has been denied, advertising tags are prevented from firing, and hits to analytics platforms are stripped of all persistent identifiers.
By embedding these protections at Gate 2, organizations maintain compliance across international data protection frameworks, supporting modern advanced analytics without regulatory jeopardy.
Gate 3: What Does the Deduplication Gate Arbitrate?
The Deduplication Gate is the synchronization layer, and the gate coordinates hybrid tracking channels so that events fired simultaneously from client browsers and cloud containers align perfectly:
* Deterministic Event Identification: Every interaction receives a unique event_id created in the browser dataLayer before tag execution. The exact string is passed to both client pixels and the server container.
* Temporal Alignment: The server records the client timestamp and validates that downstream vendor APIs receive both browser and server payloads within documented vendor deduplication windows (48 hours for Meta, 24 hours for TikTok, and 72 hours for Google Ads).
* Channel Routing Rules: The container arbitrates which events dispatch directly to third-party endpoints. In mature server-side deployments, client-side marketing tags are systematically turned off, converting hybrid channels into pure server-to-server feeds once deduplication stability reaches 100%.
Gate 4: What Does the Verification Gate Monitor?
The Verification Gate is the final monitoring layer, and the gate watches data delivery to downstream platforms and flags integration failures before they distort business reporting:
* Downstream Error Telemetry: Outbound HTTP responses from Meta CAPI, Google Ads, GA4, and TikTok are monitored for non-200 HTTP response codes. API errors (such as expired OAuth tokens, invalid parameter formats, or rate limits) are logged immediately.
* Dead Letter Queues: Failed outbound webhooks are routed to Cloud Pub/Sub queues and stored in BigQuery dead-letter tables, enabling automatic retries with exponential backoff.
* Observability Dashboards: Cloud Monitoring dashboards track container health metrics: request volume, latency distributions (p50, p95, p99), container instance counts, memory usage, and error percentages.
* Synthetic Auditing: Automated synthetic monitoring scripts execute mock purchase transactions through the staging site every four hours, verifying that event_id propagation, parameter hashing, and server delivery continue to operate without regression.
How Is an Enterprise Blueprint Deployed on Google Cloud Run?
The standard enterprise blueprint is Server Google Tag Manager on Google Cloud Platform (GCP), with Google Cloud Run, Cloud Load Balancing, and Cloud Armor providing performance, elasticity, and cost control.
The following Terraform configuration provides an enterprise baseline for deploying a production-ready sGTM environment with warm instance guarantees, automated autoscaling, and CPU allocation:
/* Production Google Cloud Run Configuration for Server GTM */
terraform {
  required_version = ">= 1.5.0"
  required_providers {
    google = {
      source  = "hashicorp/google"
      version = "~> 5.0"
    }
  }
}

variable "project_id" {
  type        = string
  description = "GCP Project ID"
}

variable "region" {
  type        = string
  default     = "us-central1"
  description = "GCP deployment region"
}

variable "container_config" {
  type        = string
  description = "Base64-encoded sGTM container configuration string"
}
resource "google_cloud_run_v2_service" "sgtm_production" {
  name     = "sgtm-prod-cluster"
  location = var.region
  ingress  = "INGRESS_TRAFFIC_INTERNAL_LOAD_BALANCER"

  template {
    scaling {
      min_instance_count = 2   /* ELIMINATES COLD STARTS */
      max_instance_count = 20  /* GUARDS AGAINST RUNAWAY AUTOSCALING BILLS */
    }

    containers {
      image = "gcr.io/cloud-tagging-10302018/gtm-cloud-image:latest"

      resources {
        limits = {
          cpu    = "1000m"
          memory = "1024Mi"
        }
        cpu_idle = false /* FORCES CPU TO REMAIN ALWAYS ALLOCATED */
      }

      env {
        name  = "CONTAINER_CONFIG"
        value = var.container_config
      }

      env {
        name  = "RUN_AS_PREVIEW_SERVER"
        value = "false" /* SPLIT PREVIEW FROM PRODUCTION FOR RESILIENCE */
      }

      env {
        name  = "PORT"
        value = "8080"
      }
    }

    max_instance_request_concurrency = 80 /* PREVENTS EVENT LOOP CHOKING */
  }

  traffic {
    type    = "TRAFFIC_TARGET_ALLOCATION_TYPE_LATEST"
    percent = 100
  }
}

resource "google_cloud_run_service_iam_member" "public_access" {
  location = google_cloud_run_v2_service.sgtm_production.location
  project  = google_cloud_run_v2_service.sgtm_production.project
  service  = google_cloud_run_v2_service.sgtm_production.name
  role     = "roles/run.invoker"
  member   = "allUsers"
}
Which Architectural Deployment Choices Protect the Container?
Three architectural deployment choices are mandatory, and each choice protects the container from self-inflicted failure. Each choice is a hard requirement rather than a tuning preference.
- Isolated Preview Server: Never run the GTM Preview server inside your primary production cluster. Configure a separate, minimal single-instance Cloud Run service for Preview Mode. Isolation prevents developer debugging sessions from consuming production compute resources.
- Internal Load Balancer Ingress: Setting ingress to internal load balancer ensures all public traffic passes through Google Cloud Load Balancing and Cloud Armor. Internal ingress shields the raw Cloud Run endpoint from distributed denial-of-service attacks.
- Warm Instance Floors: Enforcing
min_instance_count = 2ensures there is zero cold start latency during routine traffic fluctuations, maintaining sub-100ms response times for client analytics dispatches.
How Do Google Ads Enhanced Conversions and CRM Stitching Activate Server Data?
Google Ads Enhanced Conversions and CRM stitching are the offensive half of server-side tracking, because moving tracking server-side is not merely a defensive measure against cookie depreciation. Server-side data elevates conversion attribution and ad auction bidding performance under a comprehensive measurement strategy.
How Do Google Ads Enhanced Conversions Work Through a Server Container?
Google Ads Enhanced Conversions is a supplement to traditional conversion tags, sending first-party hashed customer data (email addresses, names, home addresses, phone numbers) to Google in a secure SHA-256 format. A server container is the implementation route for three performance advantages:
* Higher Conversion Match Rates: Server containers can ingest customer records directly from e-commerce backend hooks or CRM databases, appending complete billing addresses and phone numbers that are rarely accessible inside the browser dataLayer.
* Cross-Device Attribution Recovery: Google uses these hashed customer identifiers to match website conversions against logged-in Google accounts on YouTube, Google Search, and Display networks. The recovery restores conversion touchpoints that were previously lost to cross-device hops or third-party cookie blocking.
* Bidding Optimization: Smart Bidding algorithms (Target CPA and Target ROAS) depend on high conversion volumes to train their bidding models. By recapturing 5% to 15% of previously dropped conversions, the bidding engine optimizes faster, lowering effective customer acquisition costs.
How Does Offline Conversion Stitching Support Margin-Based Bidding?
Offline conversion stitching is the extension beyond client-side tags, because traditional client-side tags can only report front-end checkout completions. Client-side tags cannot track order cancellations, returns, warehouse fulfillment failures, or downstream offline sales cycles.
By connecting enterprise CRM systems (Salesforce, HubSpot) or ERP databases to the server container, organizations can orchestrate bidirectional conversion attribution:
1. Initial Form Submission: A visitor fills out a B2B demo request. The server container captures the gclid or wbraid parameter along with the user email and issues a persistent first-party lead identifier.
2. Offline Deal Progression: Thirty days later, the prospect signs a contract in Salesforce. A Salesforce outbound webhook fires a deal-won event to the server container endpoint.
3. Server-Side Egress: The server container retrieves the original click identifier and conversion timestamp, normalizes the revenue value, and transmits an offline conversion to Google Ads and LinkedIn via their Conversion APIs.
4. Profit-Optimized Bidding: Instead of bidding on raw gross revenue, the server container queries internal product databases to calculate net contribution margin (Gross Revenue minus Cost of Goods Sold and Shipping). Passing net margin as the conversion value directs Google Ads Smart Bidding to prioritize high-margin merchandise rather than high-volume, low-profit products.
Which Diagnostic Protocols Belong in a Production Auditing Playbook?
Production auditing protocols are the maintenance layer for resilient server-side tracking infrastructure. Structured diagnostic routines are mandatory, and tracking engineers should execute the following protocols before promoting any configuration to production.
Step 1: How Do You Verify Headers and Cookies With cURL?
Header and cookie verification is a terminal check with cURL. The check confirms that your custom tracking domain terminates TLS properly, returns expected HTTP headers, and correctly scopes first-party cookies without triggering ITP caps:
curl -v -I https://ss.brand.com/healthy
Key Validation Checkpoints:
* Ensure HTTP/2 or HTTP/3 is active.
* Verify the set-cookie header contains Domain=.brand.com (with the leading dot for full subdomain coverage).
* Confirm that Secure, HttpOnly, and SameSite=Lax flags are present.
* Confirm that cache-control prohibits intermediate caching of dynamic event hits.
Step 2: How Do You Audit Deduplication and PII in BigQuery?
Deduplication and PII auditing is a BigQuery job. When event telemetry streams into BigQuery, run automated diagnostic SQL queries to identify uncoordinated event_id strings and detect unhashed PII leaks across your event stream:
/* Audit Query: Detect Meta CAPI Deduplication Discrepancies and Plaintext PII */
WITH EventStream AS (
  SELECT
    event_timestamp,
    event_name,
    (SELECT value.string_value FROM UNNEST(event_params) WHERE key = 'event_id') AS client_event_id,
    (SELECT value.string_value FROM UNNEST(event_params) WHERE key = 'page_location') AS page_location,
    (SELECT value.string_value FROM UNNEST(user_properties) WHERE key = 'user_id') AS user_id
  FROM
    `enterprise-analytics-2026.analytics_320984123.events_*`
  WHERE
    _TABLE_SUFFIX = FORMAT_DATE('%Y%m%d', DATE_SUB(CURRENT_DATE(), INTERVAL 1 DAY))
)
SELECT
  event_name,
  COUNT(*) AS total_events,
  COUNTIF(client_event_id IS NULL) AS missing_event_ids,
  /* Check for unhashed email strings inside page_location parameters */
  COUNTIF(REGEXP_CONTAINS(page_location, r'(?i)[a-z0-9._%+-]+@[a-z0-9.-]+\.[a-z]{2,}')) AS pii_email_leaks,
  /* Check for unhashed US and international phone number patterns */
  COUNTIF(REGEXP_CONTAINS(page_location, r'(\+?[0-9]{1,3})?[-. ]?\(?[0-9]{3}\)?[-. ]?[0-9]{3}[-. ]?[0-9]{4}')) AS pii_phone_leaks
FROM
  EventStream
WHERE
  event_name IN ('purchase', 'generate_lead', 'sign_up')
GROUP BY
  event_name;
If missing_event_ids exceeds 0% on milestone conversion events, your client dataLayer is failing to pass unique deduplication keys before server dispatch. If pii_email_leaks or pii_phone_leaks registers any positive count, your Transformation Variables are failing to intercept form redirects, and remediation is immediate.
Which Engineering Best Practices Belong on the Pre-Launch Checklist?
Engineering best practices on the pre-launch checklist are the final gate before production. Production launch is gated by this architectural checklist:
- DNS Architecture: Custom domain is configured on an edge reverse proxy sharing the primary domain ASN and IP space.
- Container Sizing: Google Cloud Run instances configured with minimum 2 instances, CPU always allocated, and concurrency capped at 80 to 100.
- Deterministic Deduplication: A single, unique
event_idis generated in the clientdataLayerand mapped across all browser and server tags. - Cookie Security: Cookies set via the server container enforce
Domain=.brand.com,Secure,HttpOnly, andSameSite=Lax. - PII Filtering: Transformation variables scrub email, phone, and address parameters from URLs before dispatch to third-party endpoints.
- Consent Enforcement: Google Consent Mode v2 signals (
gcsandgcd) are parsed; unauthorized tags are blocked when consent is denied. - Static Asset Caching: Requests for
gtm.jsare cached at the CDN edge with a time-to-live of 6 to 12 hours. - Logging Governance: Container logging is set to error level in production, preventing runaway Cloud Logging fees.
- Dead Letter Queues: Failed egress dispatches are routed to Pub/Sub queues for automated retry handling.
- Synthetic Monitoring: End-to-end automated conversion tests run at scheduled intervals to detect regressions.
Frequently Asked Questions
Why does Meta CAPI report duplicate purchase events in hybrid setups?
Meta CAPI double-counts conversions when the client browser pixel and server payload transmit mismatched event_id or event_name parameters. Deduplication requires an identical, deterministic event_id generated in the client dataLayer before tag firing. Meta deduplicates events arriving within a 48-hour window when these identifiers match exactly.
How do you prevent Safari ITP from capping first-party cookies to seven days?
Safari caps JavaScript-set cookies to seven days or 24 hours under ITP. Configure your server-side tagging endpoint as a first-party subdomain sharing the parent domain IP namespace. HTTP Set-Cookie headers with HttpOnly and Secure flags then extend cookie lifespan, because browsers treat them as server-issued first-party cookies.
What is the optimal Cloud Run configuration to prevent cold start event drops?
The optimal Cloud Run configuration sets minimum instances to at least two. That floor prevents container scale-to-zero behavior, eliminating initial deployment pauses of 1,500 to 4,000 milliseconds. Set CPU allocation to remain always allocated rather than active only during request processing.
How does server-side tagging protect against GDPR and CCPA non-compliance?
Server-side tagging routes all hits through a private proxy container where you intercept payloads before third-party egress. Strip query string parameters containing plaintext emails, hash phone numbers with SHA-256, and halt tag firing when Google Consent Mode flags indicate denied consent. The container then blocks unlawful ad network exfiltration.
What is the difference between client-side tagging and server-side tagging for Core Web Vitals?
Client-side tagging executes third-party JavaScript libraries in the browser, inflating Total Blocking Time and delaying Interaction to Next Paint. Server-side tagging shifts endpoint requests to a single consolidated first-party stream, eliminating redundant client scripts, reducing page execution overhead, and improving mobile Core Web Vitals scores.